Reading Time: 2 minutes
Vulnerability in Canon EOS Utility – Please Update
If you registered your camera with Canon or have a Canon account, you most likely already received an email form Canon about a vulnerability in EOS Network Setting Tool which is part of the Canon EOS Utility. I used to use this software a lot in the past with my 5D MkII, now not so much anymore.
Either way, if you have it installed on your computer you should update EOS Utility immediately.
Below is the message from Canon, which also can be found on Canon’s website.
CPA2026-005: Vulnerability Remediation for EOS Network Setting Tool
June 15, 2026
Canon Inc.
Description:
Canon U.S.A., Inc. has recently identified multiple vulnerabilities in the EOS Network Setting Tool, which is included with the EOS Utility installer. If these vulnerabilities are exploited, authentication information used in the FTP/FTPS/SFTP communication test function could be obtained by a third party.
As of the date of this notice, there have been no reports of these vulnerabilities being exploited. However, to enhance the security of the product, we recommend that our customers install the latest EOS Network Setting Tool, which is included in EOS Utility.
Affected Software:
- EOS Network Setting Tool Version 1.5.0 or earlier (for Windows and macOS), which is included in EOS Utility Versions 3.12.0 through 3.20.20 (inclusive).
For details of the affected software titles and versions, please refer to your product’s Software & Drivers download page on Canon USA’s website.
Mitigation/Remediation:
EOS Utility, which includes the EOS Network Setting Tool addressing these issues, is available on Canon USA’s website. We recommend that our customers install the latest EOS Utility and confirm that the following software version is installed: EOS Network Setting Tool Version 1.5.1 or later (for Windows and macOS), which is included in EOS Utility Version 3.20.21 or later.
CVE / CVSS:
CVE-2026-9258: Improper validation of SSH host keys in the EOS Network Setting Tool. CVSS:4.0/AV:N/AC:L/AT:N/PR:N/UI:P/VC:H/VI:N/VA:N/SC:N/SI:N/SA:N Base Score: 7.1.
CVE-2026-9259: Improper validation of server certificates in the EOS Network Setting Tool. CVSS:4.0/AV:N/AC:L/AT:N/PR:N/UI:P/VC:H/VI:N/VA:N/SC:N/SI:N/SA:N Base Score: 7.1.
CVE-2026-9260: Use of hard-coded cryptographic keys in the EOS Network Setting Tool. CVSS:4.0/AV:L/AC:L/AT:N/PR:N/UI:N/VC:H/VI:N/VA:N/SC:N/SI:N/SA:N Base Score: 6.9.
CVE-2026-9261: Use of weak SSH cryptographic algorithms in the EOS Network Setting Tool. CVSS:4.0/AV:N/AC:H/AT:N/PR:N/UI:P/VC:H/VI:H/VA:N/SC:N/SI:N/SA:N Base Score: 7.6.
CVE-2026-9262: Use of a non-secure protocol as the default FTP configuration in the EOS Network Setting Tool. CVSS:4.0/AV:N/AC:L/AT:N/PR:N/UI:P/VC:H/VI:N/VA:N/SC:N/SI:N/SA:N Base Score: 7.1.
Canon would like to thank the following researchers for identifying this vulnerability:
- CVE-2026-9258, CVE-2026-9259, CVE-2026-9260, CVE-2026-9261, and CVE-2026-9262: Ryan Hausknecht (@haus3c)
Download the latest version
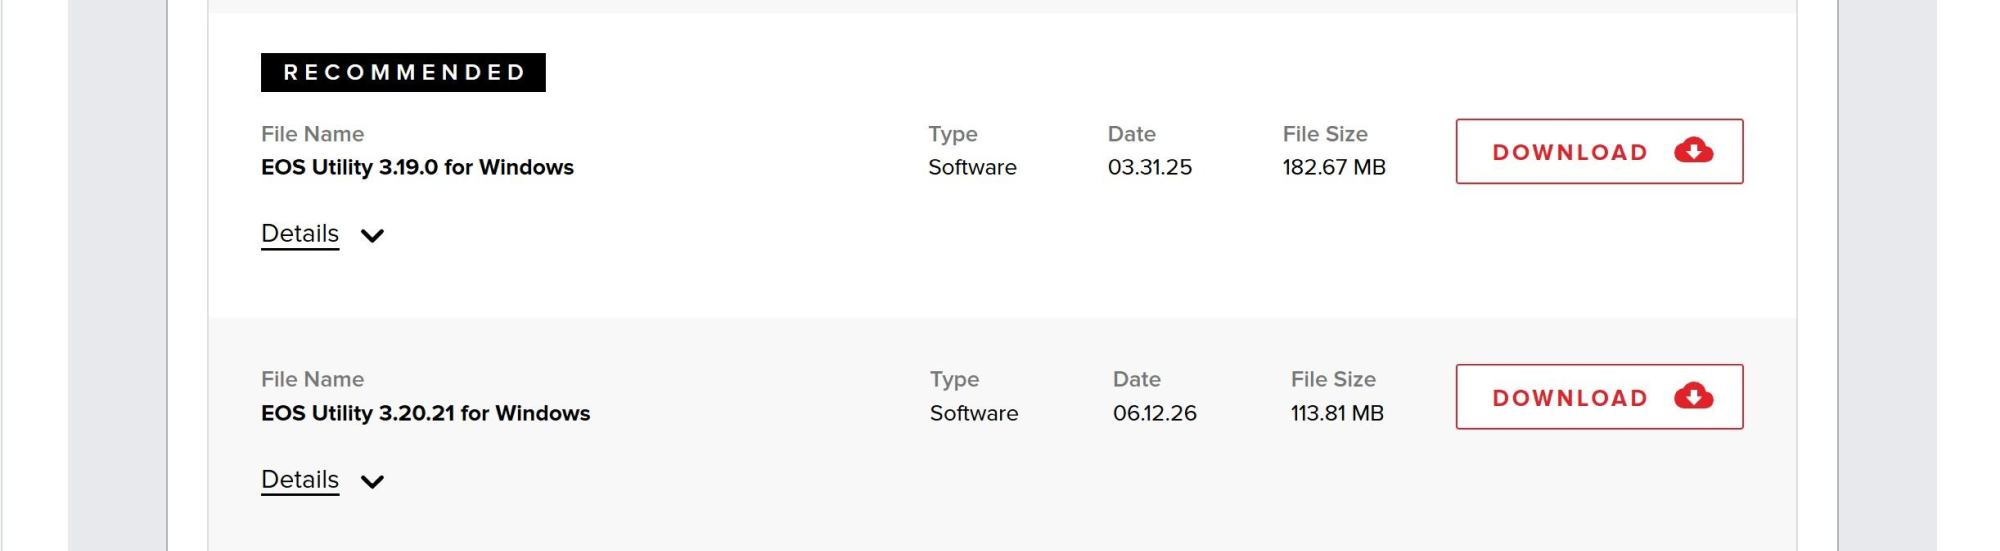
Please go to Canon’s website and download the latest EOS Utility. As of the writing of this post it is Version 3.20.21. It is the same version for both Windows and Mac.
Oddly enough, Canon’s website still shows the older, vulnerable version as “recommended”.

Peter is an award-winning photographer who travels all over the world to capture the beauty of our planet as well as the achievements of humanity. Follow Peter on his travel blog Gate to Adventures for more amazing places to go and explore.